How to Secure Your SAP Landscape Against Cyber Threats in 2026
Enterprise SAP solutions control finances, human resources, procurements, and logistics processes. Therefore, they represent attractive targets for cybercriminals. However, many companies view their SAP security measures as secondary and delegate them to projects dedicated to system migration and maintenance.
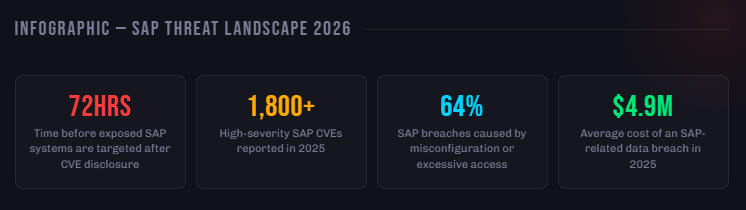
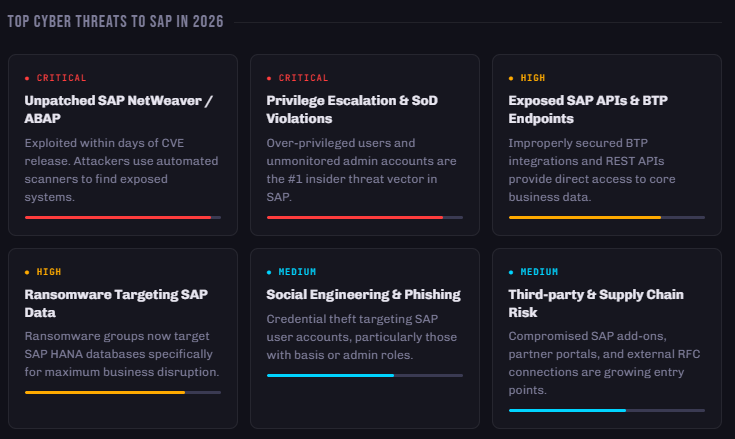
The year 2026 will require a new attitude towards SAP security. Ransomware actors target exposed SAP NetWeaver, SAP S/4HANA , and BTP infrastructures. This handbook contains all the information required for your SAP security implementation efforts.
Patch Management — Your First Line of Defense
SAP delivers its security patches on the second Tuesday of each month ("SAP Patch Day"). Still, some firms trail in implementing patches by as much as six to twelve months, leaving their systems exposed to potential attacks. Adopt a systematic approach to patches, including assessing critical notes within three days and installing within one month.
Identity, Access & Segregation of Duties (SoD)
Not surprisingly, the most abused vulnerability in SAP is human-based. Too many privileges, too many orphan accounts, and too many SoD violations make it easy for cybercriminals to exploit SAP systems after obtaining legitimate login credentials. To counter this trend, practice least privilege, review access rights quarterly, and monitor your SAP GRC Access Control tool.
· Remove access or update passwords for the SAP* and DDIC default accounts immediately after implementation of your system.
· Equip your SAP users with MFA, particularly those in the basis administration and corporate leadership categories.
· Conduct quarterly SoD conflict analysis using SAP GRC Access Control or another vendor's tool.
· Orphan accounts should be locked out or deleted.
Zero Trust Architecture for SAP Environments
The old "trust everyone inside the network" approach is obsolete. In 2026, Zero Trust is the security foundation - trust nothing and verify everything. In SAP, it will mean network segmentation to isolate SAP systems, session validation for authenticated users, and strong API Gateway controls for SAP BTP integration.
Secure SAP BTP & Cloud Integrations
Moving workloads to SAP BTP opens up new avenues for attacks to be carried out. Misconfigured subaccounts, over-permissive service keys, and exposed integration endpoints are being increasingly abused. Ensure that OAuth 2.0 is used for API authorization, rotate service keys every 90 days, and make use of SAP Analytics Cloud Identity Services for managing identities.
Continuous Monitoring & Incident Response
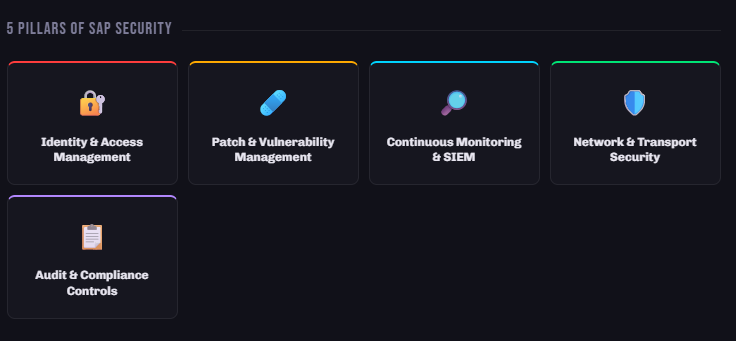
Security is not an exercise that can be carried out once. Create a continuous monitoring process whereby the audit log files from SAP are imported into your SIEM system and alerts set up for important activities like access to tables using SE16, as well as production debugging. On average, the dwell time in breaches in SAP is 146 days.

 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek