SOC Security Services for Healthcare: Avoiding Painful Compliance Failures in India
Why Healthcare Organizations Are Turning to SOC Security Services
Healthcare organizations across India are digitizing patient records, diagnostic systems, and billing platforms at a rapid pace. This shift improves care delivery and operational efficiency, but it also expands the attack surface significantly. For hospital administrators, IT managers, and compliance officers, adopting SOC security services has become as much a compliance necessity as a security decision, because patient data breaches carry both regulatory consequences and lasting reputational damage.
Why Compliance Pressure on Healthcare Security Is Rising
Healthcare data is uniquely sensitive — it includes personal identifiers, medical history, and financial details tied to insurance and billing. Regulatory frameworks such as HIPAA, which applies to organizations handling US-linked healthcare data, along with India's evolving data protection expectations, place clear requirements on how this information must be monitored, stored, and protected. Compliance officers are increasingly expected to demonstrate continuous monitoring during audits, not simply produce periodic security review documents.
Why Traditional IT Security Falls Short in Healthcare Settings
Many healthcare organizations still rely primarily on antivirus software and periodic vulnerability scans rather than continuous, real-time monitoring. This approach can miss threats in progress — such as unauthorized access attempts to electronic health records or unusual patterns in outbound data transfer that may indicate a breach already underway. Hospital IT teams are also frequently under-resourced, managing both clinical technology support and security responsibilities with limited staff, which leaves monitoring inconsistent over time.
How SOC Security Services Strengthen Healthcare Compliance
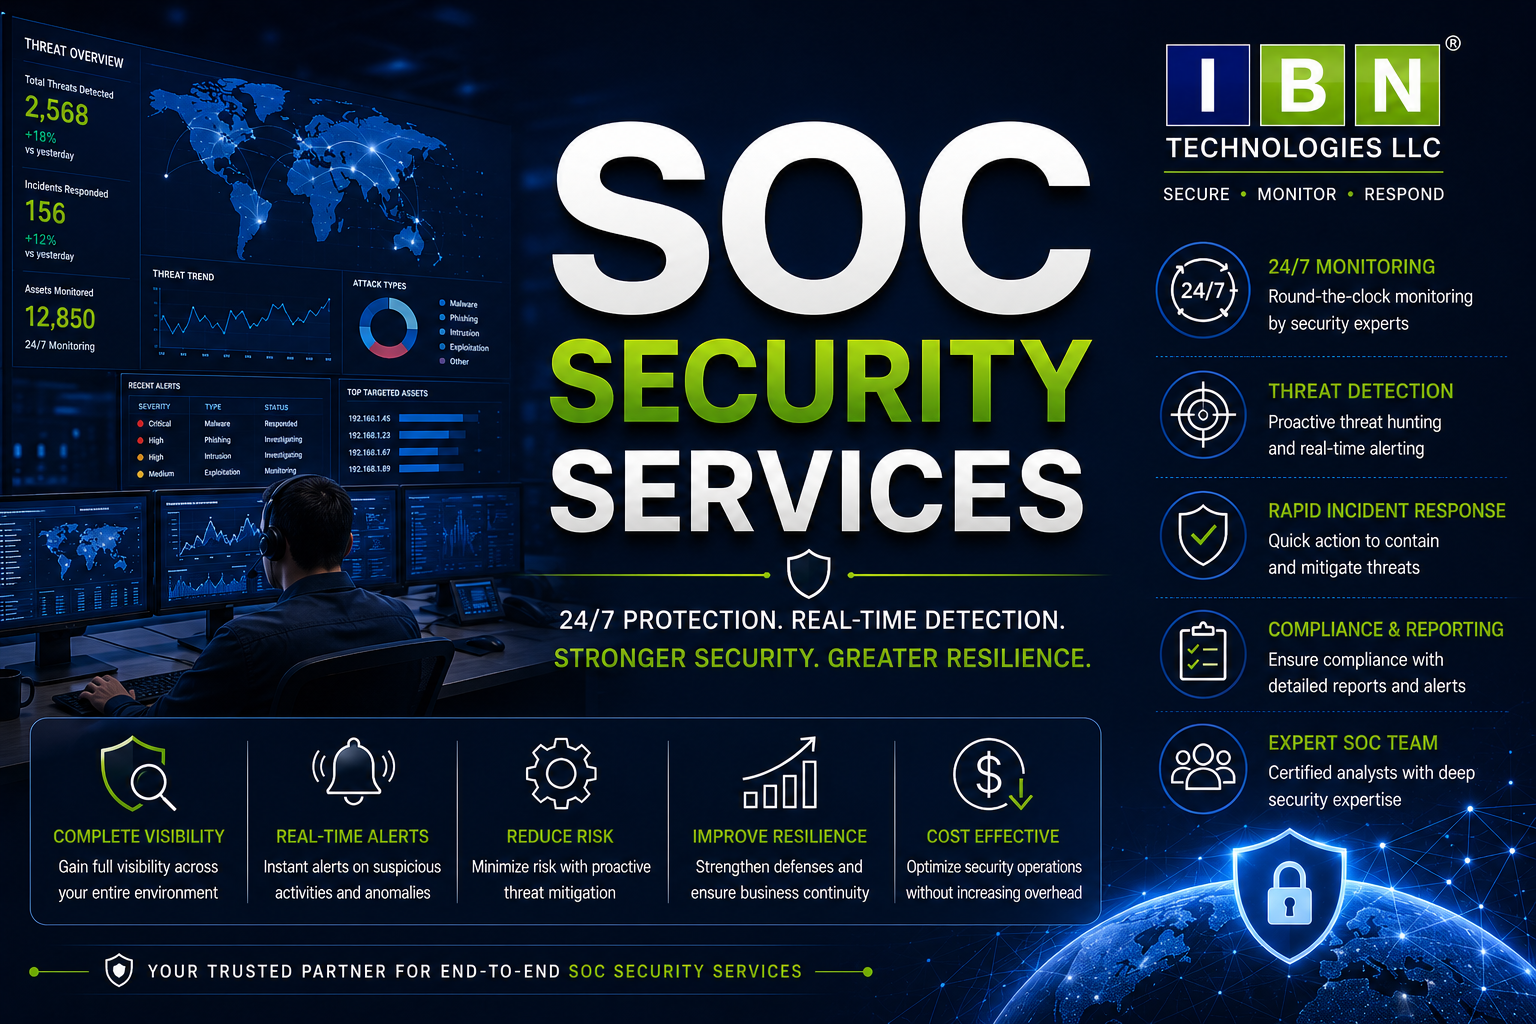
These services continuously monitor access logs, network traffic, and system activity to detect anomalies that could indicate a data breach or internal misuse. IBN Technologies' Managed SIEM and SOC services are structured to support compliance-ready security, using centralized log correlation and real-time dashboards that give compliance officers audit-ready visibility into system activity, rather than requiring manual log reviews after an incident has already occurred.
SOC Security Services Checklist for Healthcare Organizations
- Does the provider support continuous monitoring aligned with HIPAA and relevant Indian data protection expectations
- Are access logs to patient data centrally tracked and correlated across systems
- Is there a clearly defined incident response process for suspected data breaches
- Can the provider generate compliance-ready reports formatted for auditors
- Does the service scale across multiple facilities, departments, or care sites
- Is coverage genuinely available 24/7, given that healthcare systems operate continuously
Benefits of SOC Security Services for Healthcare Organizations
Continuous monitoring narrows the window between when a breach occurs and when it is detected, which directly limits the scope of patient data exposure if an incident does happen. It also relieves internal IT staff from having to manually track compliance-related activity across systems, freeing them to focus on supporting clinical technology. Just as importantly, it gives hospital leadership documented, ongoing evidence of due diligence — something that matters significantly during regulatory reviews and payer assessments.
Industry Use Case: Unified Monitoring Across Multiple Facilities
A multi-location diagnostic chain needed consistent security oversight across facilities with varying levels of internal IT maturity. By centralizing monitoring through SOC security services, the organization gained unified visibility into access patterns across every location, making it easier to identify irregular activity regardless of which facility it originated from.
Best Practices for Healthcare Leaders Evaluating SOC Security Services
Involve compliance officers early in the provider evaluation process, not just IT staff. Request sample compliance reports before finalizing any contract. Clarify how patient data will be handled during an active incident investigation to avoid creating additional exposure. Establish clear communication protocols around breach notification timelines required under applicable regulations.
Compliance Context for Healthcare Providers in India
Healthcare compliance expectations in India are tightening as digital health adoption accelerates across hospitals, diagnostic chains, and telemedicine platforms. Organizations that can demonstrate continuous, provider-supported monitoring are generally better positioned during regulatory audits and payer security assessments, particularly when handling data connected to international patients or insurance partners bound by frameworks like HIPAA.
For healthcare organizations, adopting soc security services is no longer just about preventing cyberattacks — it's about maintaining the continuous, demonstrable compliance posture that patients, regulators, and partners increasingly expect.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Romaian
 Portuguese (Brazil)
 Greek